wellnessfitpro
A Florida man who was the subject of a 2019 investigation by ProPublica was indicted last month on federal charges that he defrauded clients of his ransomware data recovery firm.
According to the Justice Department, the man, Zohar Pinhasi, told customers he could recover their encrypted files without having to pay hackers, when, in reality, he paid the ransom and charged victims a hefty fee on top.
The indictment mirrors the findings from ProPublica’s 2019 article “The Trade Secret,” which centered on Pinhasi and his scheme. The outlet found that the ransomware victims were being harmed twice: once by the hackers, who locked their targets’ files and demanded ransom, and a second time by MonsterCloud, Pinhasi’s Florida-based data recovery firm, which misled its clients about not paying ransoms.
“By falsely claiming to decrypt ransomware without paying off the ransomers, the defendant re-victimized his clients while extracting a hefty profit for himself,” U.S. Attorney Joseph Nocella said in an Oct. 7 press release. “Our Office will vigorously prosecute ransomware attackers who prey on Americans from across the world and those who cynically profit from their criminal activity.”
When ProPublica published its story in 2019, ransomware was growing into one of the world’s most pervasive cyberthreats. Hackers locked the data of governments, schools and businesses, holding the decryption key for a ransom payment, which they usually demanded in bitcoin and other types of difficult-to-trace cryptocurrency.
ProPublica’s reporting focused on how U.S. industries, from data recovery firms like MonsterCloud to insurance giants that cover ransom payments, all fueled the extortion economy. Ransomware remains a widespread threat today, and the threat to national security has grown as hackers linked to hostile foreign governments are believed to use ransomware as a cover for espionage. The prevalence of AI tools is also making it easier for attackers to spread ransomware.
Pinhasi, who went by the alias Zack Green, told ProPublica in 2019 that MonsterCloud never promised clients that their data will be recovered by any particular method. “How we do it, it’s our problem,” he told ProPublica. “You will get your data back. Sit back, relax and enjoy the ride.” He called MonsterCloud’s data recovery methods a “trade secret.”
Pinhasi hung up when reached on his cellphone this month. A message left with a representative at MonsterCloud’s office phone number and a message left with his attorney were not returned. A spokesperson for the U.S. Attorney’s Office said Pinhasi pleaded not guilty to the federal charges.
In its 2019 investigation, ProPublica interviewed MonsterCloud’s clients and ransomware experts and found that in certain cases the firm must have paid ransoms on behalf of clients. MonsterCloud’s services were particularly popular with local law enforcement agencies, who are loath to engage with or pay criminal hackers. Several interviewed by ProPublica at the time said they chose MonsterCloud to help them recover from ransomware because they believed the firm would never pay a ransom.
Pinhasi, who described himself to ProPublica as a former IT security intelligence officer for the Israeli military, said in 2019 that MonsterCloud handled up to 30 calls a day and had about 20 employees in South Florida as well as extensive global contacts.
Federal investigators found that, over the course of the scheme, Pinhasi allegedly charged clients more than $19 million and paid more than $8 million in ransom payments. In one example, Pinhasi made a ransom payment of about $8,200 but charged the client about $150,000. If convicted, he faces up to 20 years in prison.
In the Justice Department’s October press release, an FBI official said Pinhasi had “turned the victim’s crisis into his own profit center. This deception is unacceptable, and the FBI is committed to ensuring accountability for those who choose to victimize the very people who trusted them for help.”
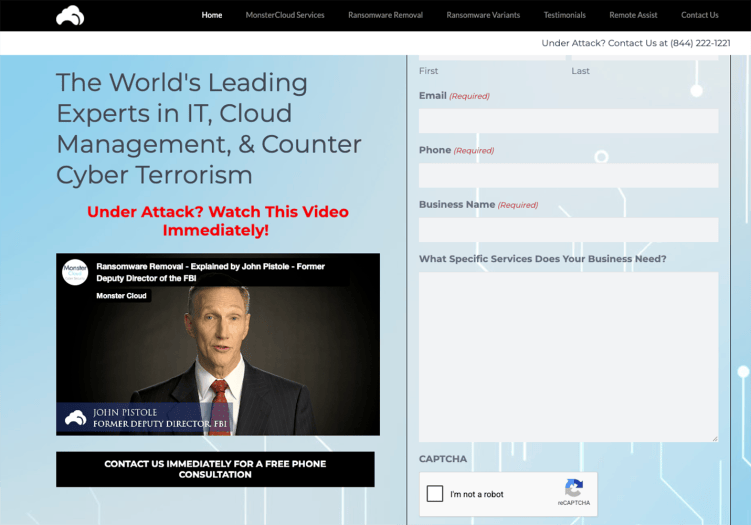
The Justice Department did not address ProPublica’s 2019 finding that one of the FBI’s own was among Pinhasi’s associates at MonsterCloud. John Pistole, a former deputy director of the FBI under Robert Mueller, was prominently featured in a promotional video on MonsterCloud’s homepage. “Police departments, government agencies, hospitals, small business and Fortune 500 firms trust MonsterCloud to help recover from attacks and protect against new ones,” Pistole said in the video. “MonsterCloud’s proprietary technology and expertise protects their professional reputations and organizational integrity.”
Pistole was not mentioned by name in the Pinhasi indictment.
In 2019, Pinhasi touted MonsterCloud’s ties to law enforcement as evidence of its integrity. Pistole, who also headed the Transportation Security Administration under President Barack Obama, was listed on MonsterCloud’s website as the only member of its “Cyber Security Advisory Council.”
Pistole did not respond to a request for comment for this story. In a 2019 interview, he said he became acquainted with Pinhasi after MonsterCloud reached him through a speaker’s bureau and that MonsterCloud paid him indirectly through that group. He said Pinhasi scripted his testimonial and that he was well aware that in most cases — including MonsterCloud’s — the only way to decrypt data locked by ransomware is to pay the hackers. “That’s the business model as I understood it,” Pistole told ProPublica at the time. “Based on my experience and knowledge, ransom is paid and they facilitate the best practices moving forward.”
A spokesperson for the U.S. Attorney’s Office declined to comment on Pistole’s connection to MonsterCloud.
#MonsterCloud #CEO #Indicted #Federal #Fraud #Charges #Data #Recovery #Scheme #ProPublica